

Enterprises, tenancy and organization workspaces
One product serves many organizations; a single sign-in never means holding all of any organization's data. Organization, permission and data boundaries come first; deeper enterprise collaboration follows step by step.
In developmentNot availableVerified
 (open full-size figure)
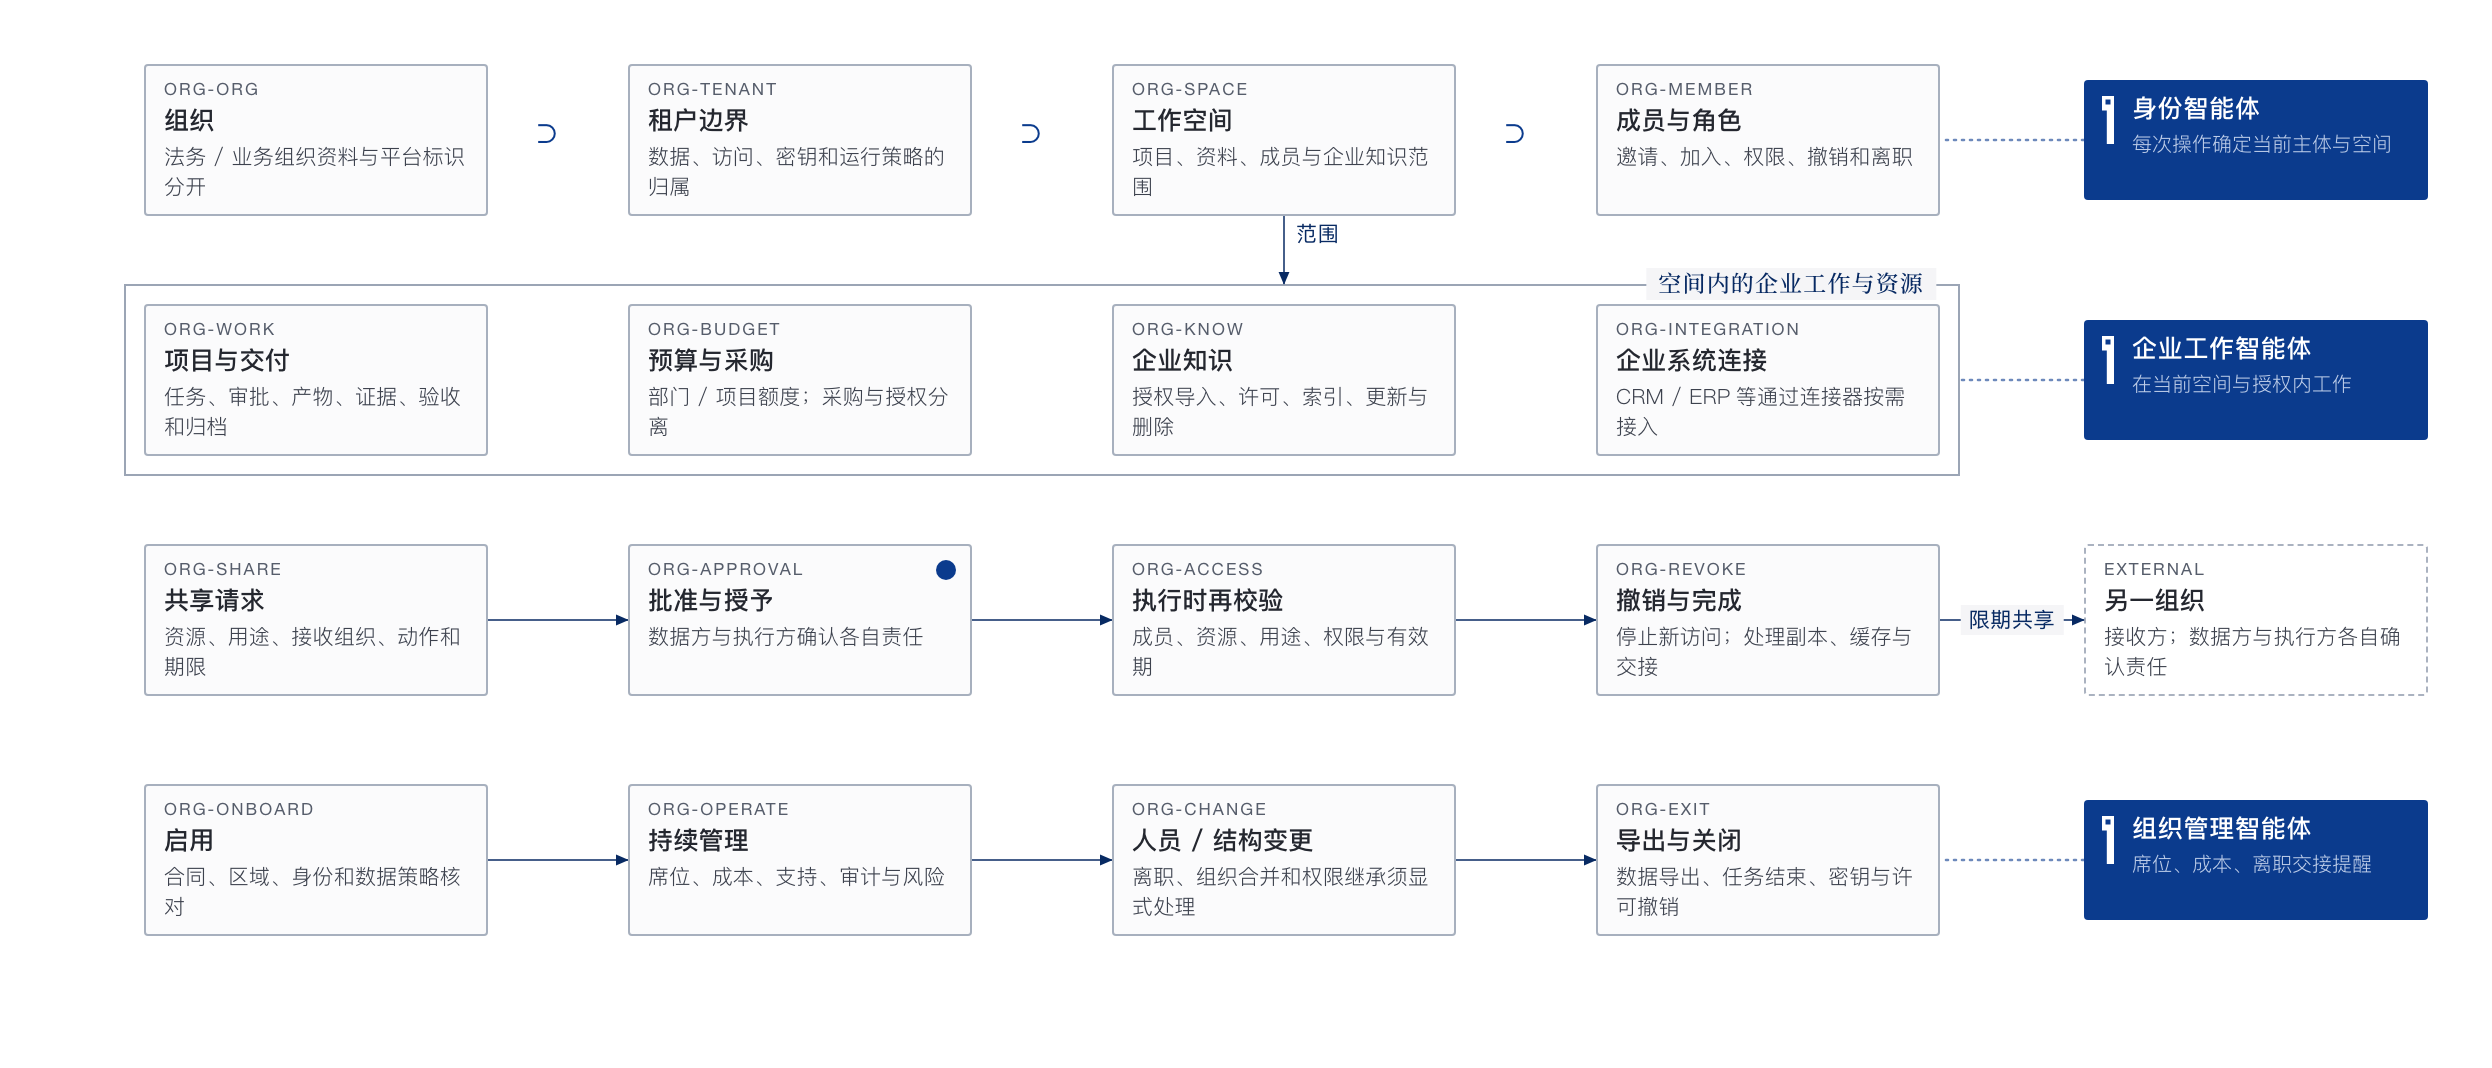
What this map shows
This is MYRILUM's target architecture. It does not mean everything on the map is live; whether a capability can be used today is stated in “Current availability”.
One product can serve many organizations; a single sign-in never means owning all of any organization's data.
First get organization, permission and data boundaries right, then deepen enterprise collaboration step by step.
Organizations and identity
| Organization | Legal and business details are kept apart from platform identifiers |
|---|---|
| Tenant boundary | Owns data, access, keys and run policies |
| Workspace | Scope of projects, materials, members and organization knowledge |
| Members and roles | Invitation, joining, permissions, revocation and leaving |
Enterprise work and resources
| Projects and delivery | Tasks, approvals, artifacts, evidence, acceptance and archiving |
|---|---|
| Budgets and procurement | Department and project credits; procurement kept apart from authorization |
| Organization knowledge | Authorized import, permissions, indexing, updates and deletion |
| Enterprise system connections | CRM, ERP and other systems connect as needed through connectors |
Cross-organization collaboration by explicit sharing
| Sharing request | Resource, purpose, receiving organization, actions and time limit |
|---|---|
| Approval and grant | The data side and the executing side each confirm their responsibilities |
| Checked again at run time | Member, resource, purpose, permission and validity |
| Revocation and completion | Stops new access; handles copies, caches and handoffs |
The enterprise lifecycle
| Onboarding | Contract, region, identity and data policy are checked |
|---|---|
| Ongoing management | Seats, cost, support, audit and risk |
| People and structure changes | Leavers, mergers and inherited permissions are handled explicitly |
| Export and closure | Data export, ending tasks, and revoking keys and permissions |
Source
This page follows A13 of the MYRILUM architecture map v2.2 (public edition: restricted products and internal open items are left out). Related: “Identity, authorization and access decisions”; “Data and memory lifecycle”; “Regions, disaster recovery and exit”.
Was this page helpful?
Opens a prefilled email to info@myrilum.com in your mail app; you decide whether to send it, and it never passes through this site. Do not include passwords or other sensitive information.
Sources and maintenance
- Region
- Global
- Version
- 0.1.0
- Publication
- Published globally
- Document status
- Approved · Drafted
- Authorization
- Public information
- Command authority
- None
- Type
- Concept
- Audience
- Technical leads, Developers, Organization leaders, Integration partners, Agents
- Safety class
- Informational
- Agent tasks
understand_platform_architecture- Owner
- Web3Capital Documentation Steward
- Last verified
- 2026-09-23
- Review due
- 2026-10-23
- Source commit
6b41cce4496d- Canonical authority
SRC-ARCHITECTURE-ATLAS-V2-2- Content digest
3ca63810e65600eb- Stable citation
MYRILUM-DOC-ARCH-013@0.1.0:en#overview
Machine-readableMarkdownMetadataJSON-LDChunks
This documentation grants no execution, release, or production authority.
Sources and maintenance
- Region
- Global
- Version
- 0.1.0
- Publication
- Published globally
- Document status
- Approved · Drafted
- Authorization
- Public information
- Command authority
- None
- Type
- Concept
- Audience
- Technical leads, Developers, Organization leaders, Integration partners, Agents
- Safety class
- Informational
- Agent tasks
understand_platform_architecture- Owner
- Web3Capital Documentation Steward
- Last verified
- 2026-09-23
- Review due
- 2026-10-23
- Source commit
6b41cce4496d- Canonical authority
SRC-ARCHITECTURE-ATLAS-V2-2- Content digest
3ca63810e65600eb- Stable citation
MYRILUM-DOC-ARCH-013@0.1.0:en#overview
This documentation grants no execution, release, or production authority.